 Author :
Traditional credential management systems often struggle with issues like forgery, data mismanagement, and complex verification processes. Verifiable credentials (VCs) are designed to address these problems with a more secure and efficient approach.
In this blog, we’ll break down what verifiable credentials are, how they work, and why they’re rapidly becoming the gold standard for modern credentialing.
Understanding Verifiable Credentials
Verifiable credentials contain an issuer’s claims about a person, organisation or other subject. A compatible verifier can check cryptographic integrity and issuer information using the required verification resources. That check does not independently establish that every claim is true or identify the person presenting it.
What makes them different from traditional physical credentials, or even their digital equivalents, such as PDFs or other digital formats, is the way they are secured. A verifiable credential follows standards such as the W3C Verifiable Credentials standard or Open Badges 3.0, which are globally recognized frameworks for data integrity and security.
A credential follows its applicable data model and securing mechanism. Blockchain storage is not required by the W3C Verifiable Credentials Data Model. Cryptographic verification can detect changes to protected data; it does not physically prevent copying, editing or misuse of a file.
Why Do Verifiable Credentials Matter – The Benefits of Verifiable Credentials
Verifiable credentials offer a wide range of practical benefits for both issuers and recipients, making them a compelling alternative to traditional options. Below are some key reasons why verifiable credentials matter:
Tamper-Evident Integrity:
Altering signed data causes its cryptographic verification to fail. Verifiers must still check issuer authority, applicable credential status and any identity requirements.
Verification Against Available Resources:
Compatible verifiers can check a credential without asking a human issuer to inspect every request. Required keys, schemas and status resources must remain available or be retained through an appropriate verification arrangement; response time is implementation-dependent.
Automation and Efficiency:
With CertifyMe, institutions can automate an approved issuance workflow. Authorised award decisions, recipient validation, access permissions and corrections remain governed responsibilities; automation does not eliminate them.
Easy Sharing and Visibility:
In most cases, credentials are meant to be shared or displayed. Verifiable credentials allow recipients to add them to LinkedIn profiles, resumes, email signatures, or digital portfolios, thereby enhancing visibility and discoverability.
The Working of a Verifiable Credential
Let us now look at how verifiable credentials function and why they are more secure than traditional systems. To begin, it is important to understand the parties involved in the verifiable credential lifecycle.
Parties Involved in a Verifiable Credential Model
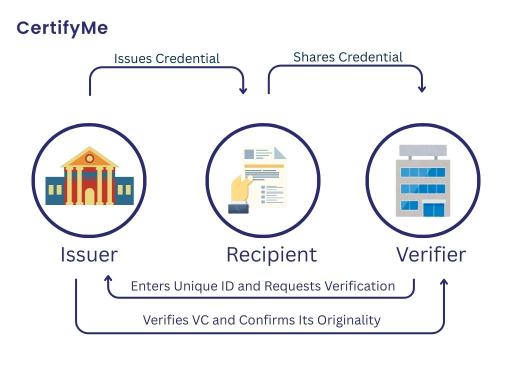
Consider the example of a student who receives a degree/credential from their university and later shares it with an employer during a job application. In this case, the parties involved are as follows:
The Issuer
It is the organization that issues the verifiable credential, in this case, the university. The issuer uses a digital credentialing software such as CertifyMe to create and issue the credential by entering the relevant recipient’s details. These details are referred to as metadata.
The Recipient
The student who receives the degree is the recipient. The recipient receives the credential via email, which includes a URL to access the verifiable credential. The recipient also receives access to a digital wallet, a secure space for storing verifiable credentials.
The Verifier
In this scenario, the verifier is the employer to whom the student has applied for a job. Once the student shares the digital degree, the employer can verify its authenticity through due procedure. For example, if the credential is issued using CertifyMe’s platform, the verifier can authenticate the credential through one of 3 ways :-
- Through ID-Tagging
- Through Cryptographic signatures
- Through OTP
Components of a Verifiable Credential
In addition to the parties involved, a verifiable credential consists of three main components:
Metadata: Metadata refers to verified information about the issuer, the recipient, and the credential itself. This data is not directly visible to third parties and is cryptographically signed to ensure security.
Claim: It is the statement that the verifiable credential makes about an individual, organization, or entity. For example, an academic degree serves as a claim that the recipient has completed a specific course of study.
Proofs: Proofs are the cryptographic and security mechanisms that protect the credential from forgery and enable verification of its originality when required.
Verifiable Credential Verification Process
Now that we understand the verifiable credential model, the verification process works as follows:
Blockchain Ledger
When the issuer creates a credential, it is anchored to a blockchain ledger. This ledger ensures immutability (permanence) while maintaining decentralization. Think of it as having multiple small boxes of information connected as nodes. If someone tries to edit information in one box, the other boxes will not accept the change.
Asymmetric Encryption
Another method used to verify a verifiable credential’s originality is asymmetric encryption, also known as a cryptographic signature.
This mechanism acts as a lock that protects the credential’s critical metadata from unauthorised third-party access. Only the issuer can unlock this information. When a verifier requests authentication, the issuer validates the credential against the blockchain ledger and confirms its authenticity.
This model enables verifiable credentials to function as a form of zero-knowledge proof, meaning the authenticity of a credential can be confirmed without revealing any personal information.
Use Cases of Verifiable Credentials
Verifiable credentials are transforming how organizations across industries issue, manage, and validate achievements and qualifications. Some of the most prominent use cases include:
-
Higher Education: Universities and colleges issue digital diplomas, transcripts, and certificates that can be instantly shared and verified by employers or other institutions.
-
Corporate Learning and Development (L&D): Organizations use digital badges and certificates to track employee skill development, training completion, and internal promotions.
-
E-learning Platforms: Online education providers award course completion certificates and micro-credentials that learners can showcase on professional networks and job platforms.
-
Professional Associations: Membership credentials, continuing education credits, and professional certifications are issued digitally to improve accessibility, renewal, and verification.
Conclusion
Upon reflection, it becomes clear that verifiable credentials represent a modern, secure, and efficient approach to issuing and validating achievements. As we continue to advance in an era of digitization, verifiable credentials are well-positioned to replace traditional credentialing systems.
As credentialing becomes increasingly digital and decentralized, understanding and adopting these secure systems will be essential for individuals and organizations seeking to remain credible and verifiable.
Review available plans and run a pilot against your institution’s issuance, verification and integration requirements. Talk to our team about the workflow you need.